
 banning-routers-wont-fix-bad-security
Banning Routers Won’t Fix Bad Security
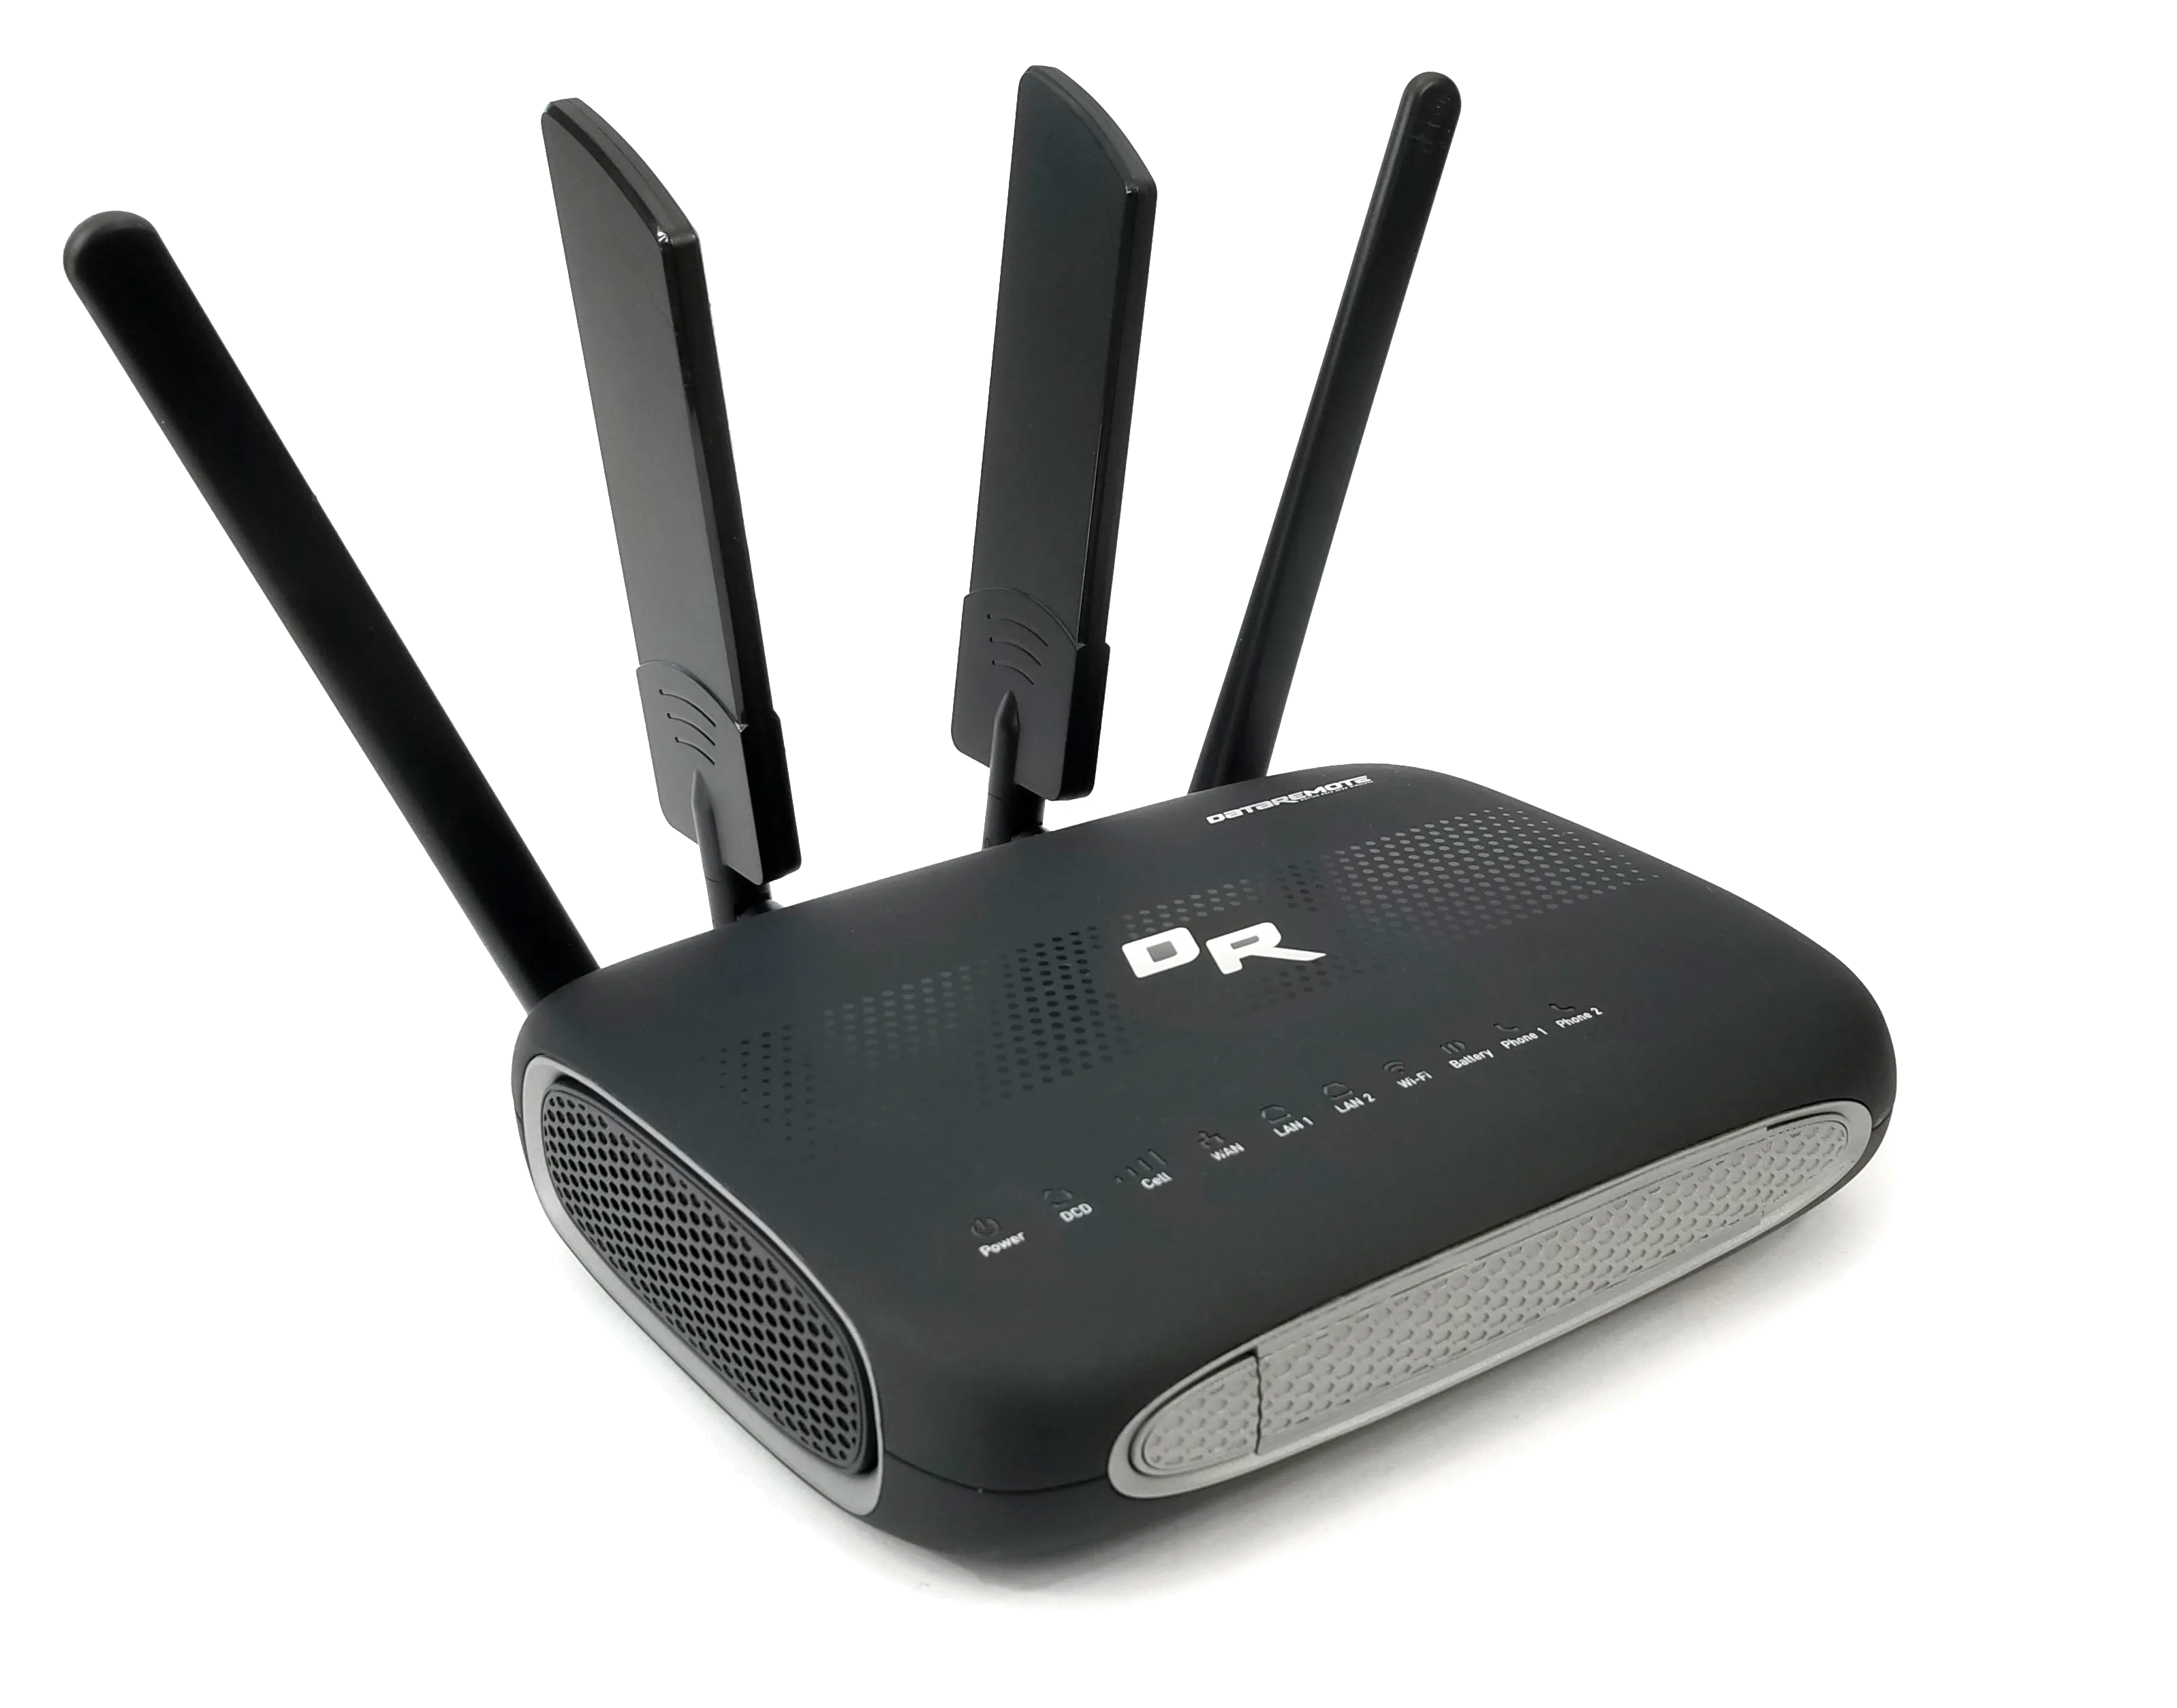
The United States wants routers that aren’t built in the USA to go through an approval process before they can be sold here. I’m not sure anyone in DC is aware of how things are made these days, but most companies rely on labor in China to make their products.
When the news first broke (TechRadar), everyone was freaking out. As they should, I mean. What isn’t built in China? So now we have to find a way to make routers in the US. I’m not opposed to the decision itself. I’m just frustrated by the timeline and the lack of thought that went into it.
According to TechRadar:
“It’s part of a wider movement by the US to reduce its reliance on other countries for hardware and software. The FCC’s statement pointed to a series of recent cyberattacks – including Volt, Flax, and Salt Typhoon – that involved foreign-made router technology.”
Let’s look at Salt Typhoon as an example. The CVEs tied to it involve networking software and hardware from Ivanti, Palo Alto Networks, Cisco, Microsoft, Fortinet, Citrix, and Sophos. CVE-2023-20273, for instance, was an attack against the web admin interface. Why are we still leaving admin pages bare-ass on the internet?! I thought we learned that lesson back in 1995 with the movie Hackers, along with not making our passwords “love,” “secret,” “sex,” and “god.”
That’s just one example of a stupid human mistake, and now someone in DC thinks, “Oh yeah, we’ll just stop allowing foreign routers to be sold in the USA.”
I also worry about the amount of e-waste this will create. The good news, as far as I’m aware, is that we can keep using the routers we already have, and they can keep getting security updates until at least January 2029.
Meanwhile, The Register reports that a “US military contractor open sources tool for validating hidden communications networks.” It’s a software toolkit built for DARPA to test covert networks, and now anyone can use it. According to the team:
“HCS designers using Maude-HCS need only ‘specify protocol behavior, adversary observables, and environmental assumptions,’ and Maude-HCS will generate results based on a range of scenarios that ‘can be used to audit claims of undetectability.’”
Now, I’ve been in tech since I was about 4 feet tall, but what this software does exactly is a little over my head. From reading The Register’s article, it can essentially spot “sneaky” activity that organizations might not otherwise notice. You’d think we could use it on our own networks to look for strange traffic. Oh wait, we can? But we still don’t trust the routers from China? Confusing, I know.
Finally, per CNET:
“Following President Trump’s leadership, the FCC will continue to do our part in making sure that US cyberspace, critical infrastructure and supply chains are safe and secure,” said FCC Chair Brendan Carr.
BTW, according to The Verge, Brendan Carr is a dummy. In my view, he’s just a yes man, like most people in government no matter what political side you’re on. Most of the decisions made in DC are about helping someone’s wallet, rather than asking people who actually know tech, or appointing someone to advise the government on tech, and, big key word, LISTENING to them. I’ve seen some of them out there helping, like Cathy Gellis. God bless her. “Trust your technologist.”
If we want to start securing things, the first step should be for software companies to use tools like Claude Code to find security vulnerabilities and exposures. LLMs are great for running probe tests against your own networks, hardware, and software. I don’t agree with how LLMs were created, using human-made images and text without people’s knowledge or approval. But the tool is here, and the “nuke” has been released. We know about it, and if it’s used properly, it can be a great tool. That whole conversation is a blog post for another time.
 Continue Reading